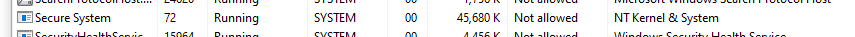Cybercrime reporting poll

pexels-donald-tong-143580

I’ve created an anonymous public poll asking the question:

Are you reporting cybercrime incidents, like ransomware, to government or police authorities?

which is here:

https://forms.office.com/r/mENdwmaXRj

as the results rolling you can see the summary here:

http://bit.ly/ciapoll01

I’m interested to see what people are doing when it comes to reporting incidents to authorities?

Exchange user best practices script

image

I’ve created a new Exchange user best practices summary script which you can find at:

https://github.com/directorcia/Office365/blob/master/o365-mx-usr-all.ps1

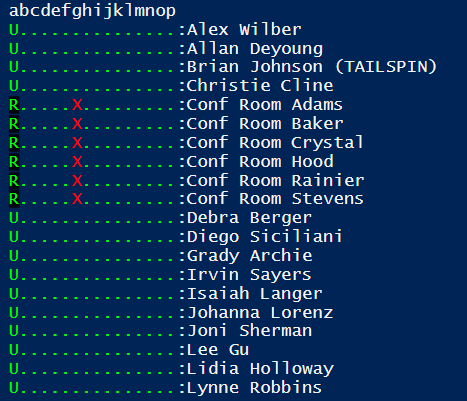
The idea with this script is to give you a quick visual summary of your user mailboxes to ensure they conform to best practices.

When you run the script without any command line options you will see the above output. Each row is a user with their name at the end of the line. The entries on the right provide you an indication of settings status. A green dot is for good and a red X is for bad. You will see this creates a matrix of settings for each mailbox. These settings are designated by a letter (currently a through p). These letters correspond to the following settings:

a = Mailbox type: S = Shared, R = Resource, U = User
b = Enabled
c = Inactive
d = Remote PowerShell Enabled
e = Retain Deleted Items for at least 30 days
f = Deliver to Mailbox and Forward
g = Litigation Hold Enabled
h = Archive Mailbox Status
i = Auto-expanding Archive Enabled
j = Hidden From Address Lists Enabled
k = POP Enabled
l = IMAP Enabled
m = EWS Enabled
n = EWS Allow Outlook
o = EWS Allow Mac Outlook
p = Mailbox Audit Enabled

image

If you use the –verbose command line option, you’ll get additional information about the script operation as you see above.

If you use the –debug command line option, a log file of the script process will be created in the parent directory.

If you use the –prompt command line option, the script will wait after each user for you to press ENTER.

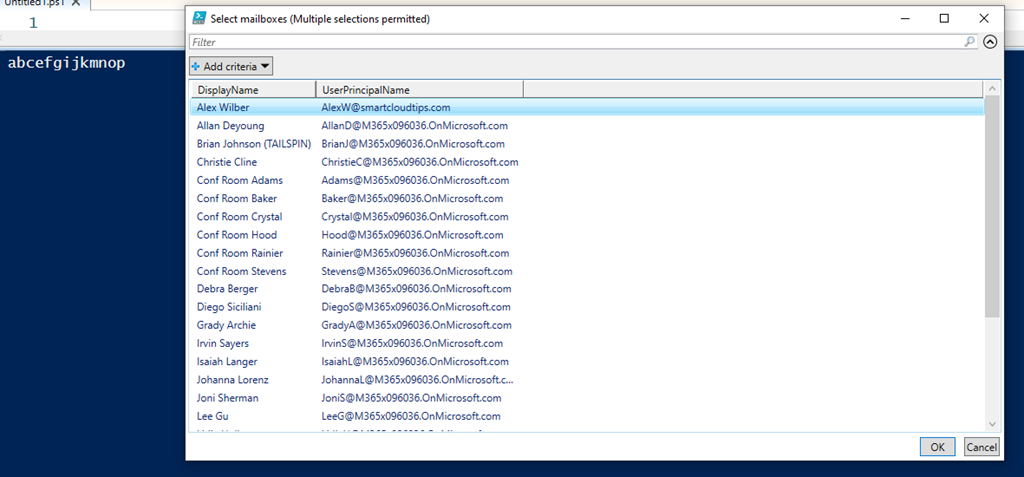
If you use the –select command line option, the script will prompt you to select the users you wish to display.

If you also specify any letter from, currently, a through p on the command line, those settings will not be checked by the script. Thus, specifying dhl on the command line will not check or display Remote PowerShell Enabled (setting = d), Archive Mailbox Status (setting = h) or IMAP enabled (setting = l).

Thus:

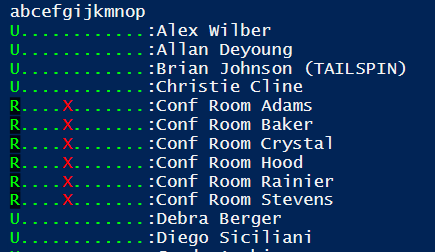
.\o365-mx-usr-all.ps1 dhl

will display:

image

(note: no d, h or l in the output)

and

.\o365-mx-usr-all.ps1 dhl –select

will display:

image

no d, h or l settings as well as prompting for selection of users to check and display.

The script requires that you are connected to Exchange Online first via PowerShell prior and this can be done using my script:

https://github.com/directorcia/Office365/blob/master/o365-connect-exo.ps1

In summary then, this script when run without any command line options is designed to give you a quick reference to your user mailboxes and whether they have best practice settings enabled. You can also run the script with number of different command line options to create a log, individually select users and settings to test as well as pause after each user if desired.

I’ll continue to update and improve this script over time so make sure you follow my Office 365 GitHub repository, which you can find here:.

https://github.com/directorcia/Office365/

Prevent alerts from DiscoverySearchMailbox

image

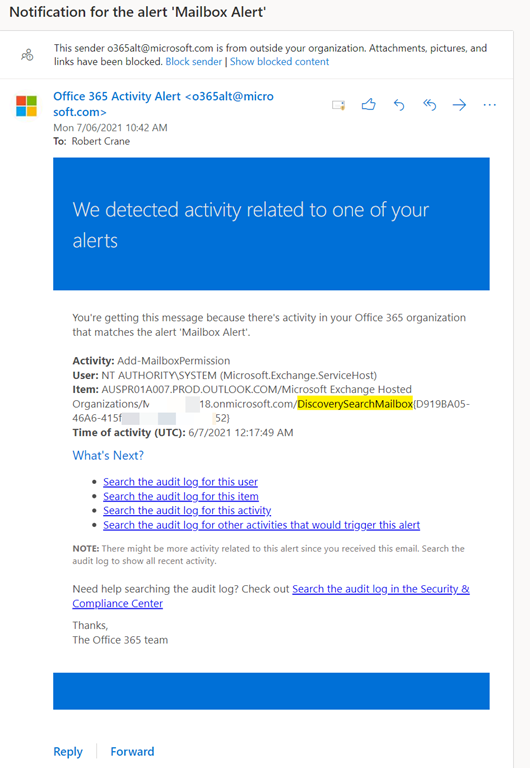
When you set up bulk alerting for mailboxes you may end up enabling alerts for system mailboxes like DiscoverySearchMailbox as shown above. This will mean receiving regular alerts about changes to that mailbox by the system. This basically means Exchange Online is performing some expected administrative process on a mailbox, which triggers a configured alert.

To reduce the noise caused by these alerts you can do the following to disable it:

image

Firstly connect to Exchange Online using PowerShell. My script for that is here:

https://github.com/directorcia/Office365/blob/master/o365-connect-exo.ps1

next run the command to find any DiscoverySearchMailbox

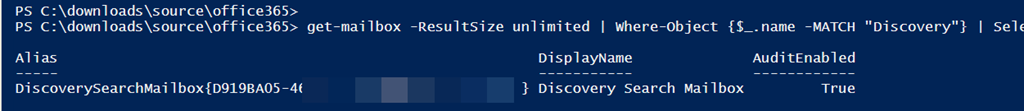
get-mailbox -ResultSize unlimited | Where-Object {$_.name -MATCH “Discovery”} | Select-Object alias, displayname, auditenabled

which should give you a result like shown above.

$dsm = get-mailbox -ResultSize unlimited | Where-Object {$_.name -MATCH “Discovery”}

Run the above command to save the mailbox details to a variable. Then run:

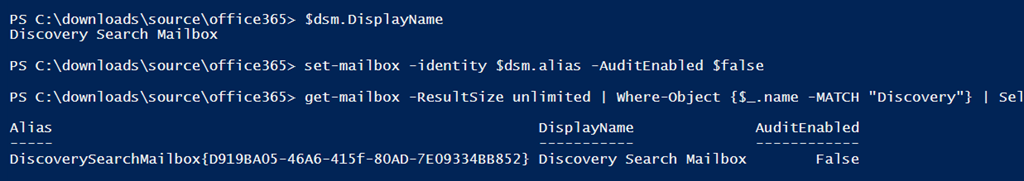
set-mailbox -identity $dsm.alias -AuditEnabled $false

to disable auditing for that mailbox.

image

if you now re-run

get-mailbox -ResultSize unlimited | Where-Object {$_.name -MATCH “Discovery”} | Select-Object alias, displayname, auditenabled

you should find that the auditing is now disabled for that mailbox as shown above.

Microsoft Teams Webinars not allowing registrations for everyone

I have been looking forward to the new Teams Webinar functionality. So as soon as I saw it appeared in my tenant I was keen to implement it.

image

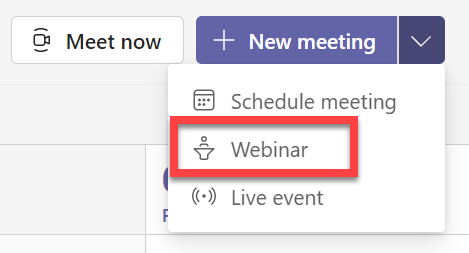
I went to the calendar app inside Microsoft Teams and displayed all the meeting options available in the top right as shown above. In there I could see that I had the Webinar option, which mean that I was in theory good to set up a webinar.

image

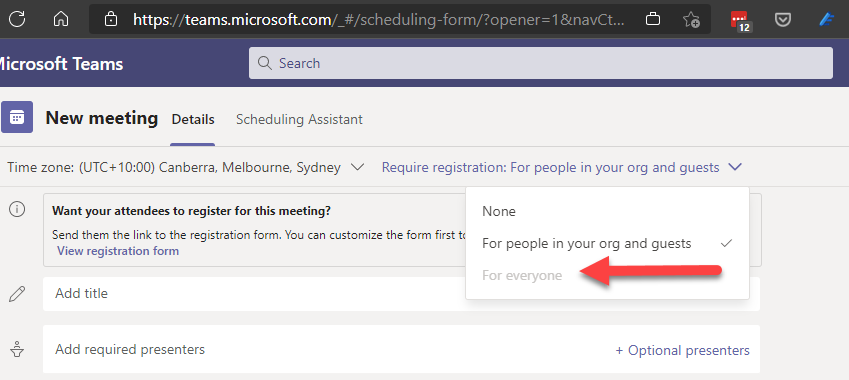
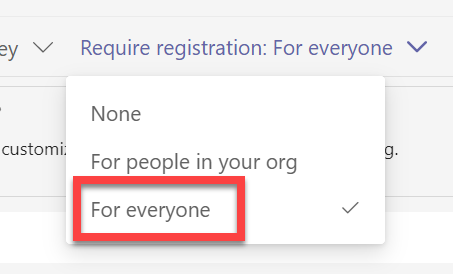
However, I discovered I had a problem that I couldn’t require registration For everyone as shown above. The  option was greyed out!

A little digging revealed this article:

Set up for webinars in Microsoft Teams

which indicated I need to run the following PowerShell commands:

Set-CsTeamsMeetingPolicy -AllowPrivateMeetingScheduling $True

and

Set-CsTeamsMeetingPolicy -WhoCanRegister Everyone

to allow anyone, including anonymous users, to register for webinars.

So, I ran these commands and waited, and waited, and waited but the For Everyone option would still not allow selection??

After much investigation here is what solved the issue for me.

I went into the Teams administration area and selected Users on the left or you can use the direct link:

https://admin.teams.microsoft.com/users

I then found the user in my tenant I wanted to check and select them.

image

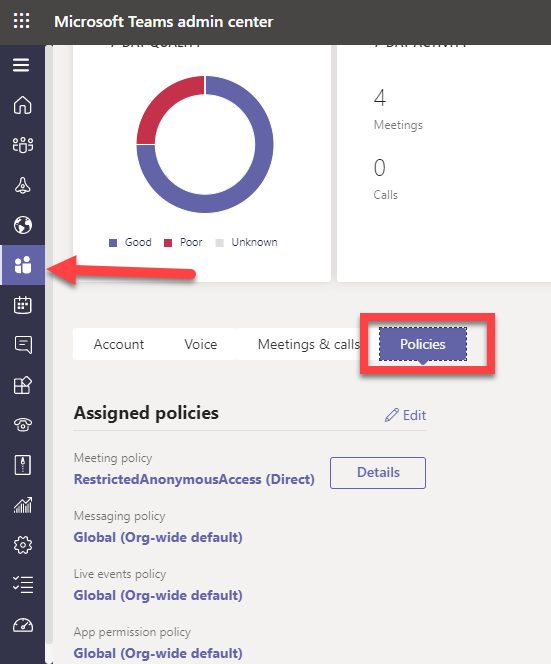
I then selected Policies from the menu in the middle of the page as shown above.

image

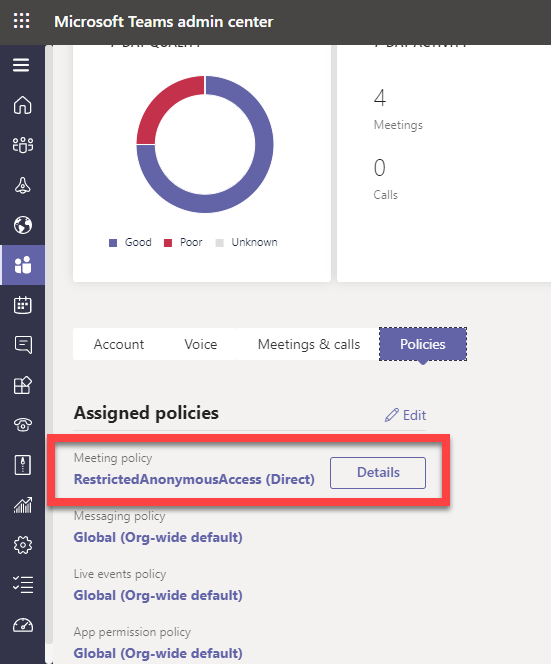
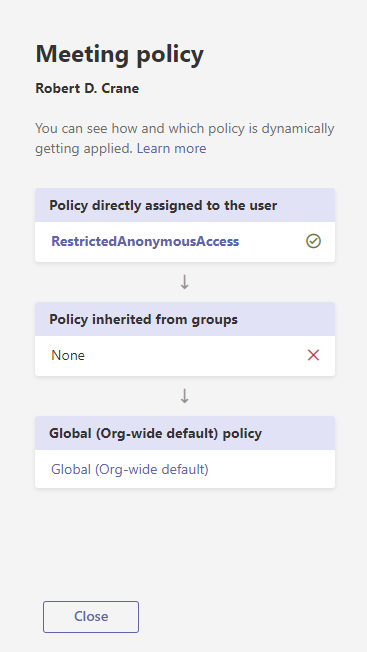
In my case, you’ll note that the Meeting policy is set to RestrictedAnonymousAccess (Direct) as shown. I then selected Details button and the following dialog appeared from the right:

image

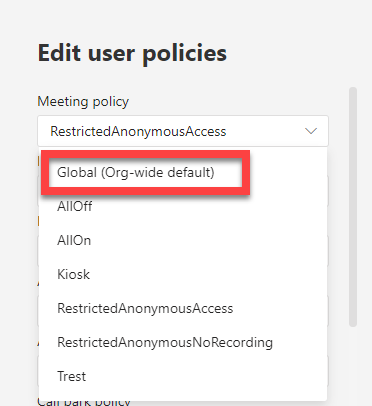
RestrictedAnonymousAccess didn’t sound like the right option to have set, so I closed that dialog and selected the Edit button to change the policy assignments.

image

I changed the Meeting policy option to Global (Org-wide default) from the list that appeared and saved the changes.

image

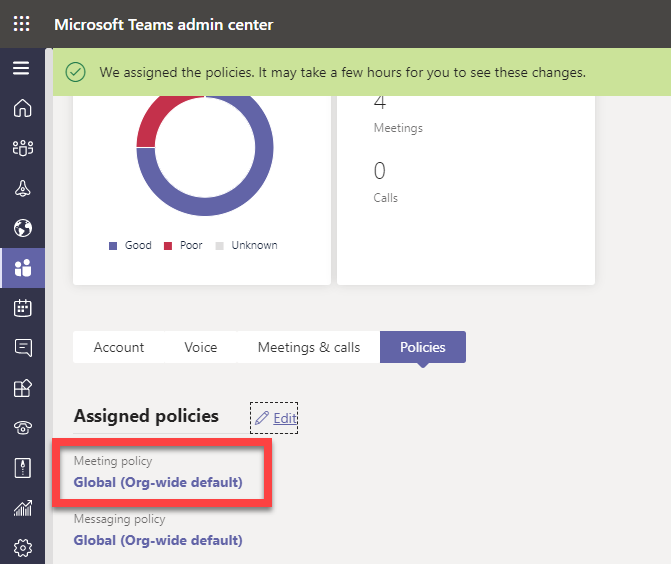
I received an assignment message at the top of the screen and the Meeting policy value changed to Global (Org-wide default) as shown above.

image

After about one hour or so I could now see the For Everyone option in the Teams webinar registration section could be selected and I was good to go!

I have no idea why the Meeting policy had changed from Global To Restricted but I found the same configuration on another tenant I have. It may have something to do with the security I set up for my environments. Not sure. However, hopefully, if you see the same issue you now know where to look to get it sorted!

CIAOPS Need to Know Microsoft 365 Webinar – June

laptop-eyes-technology-computer

I think we should  try something a little different this month for the session. I’m going to attempt to use the new Microsoft Teams Webinars feature. For anyone who has attended a previous session this means the registration process will look a little different, but in the end it should achieve the same result but with less manual work by me. To start with you need to navigate to:

http://bit.ly/n2k2106

and submit your registration details. Shortly after this you should receive an automated email from Microsoft Teams confirming your registration, including all the event details as well as a calendar invite!

How this all works come webinar time I’m still working out, but hopefully I should be across it all before the webinar starts. However, I’m sure there will be things that I’ll learn during the process, so if you want to see what unfolds then you best register to find and be part of the inaugural CIAOPS Teams webinar!

The topic for this month will be Device Management. I’ll dive into how you connect and manage devices in Microsoft 365 including iOS, Android and Windows devices. You’ll see how Microsoft 365 Device Management is a great way to improve the security of your information environment. As always, I’ll also share the latest news and events from Microsoft and as always, there’ll be plenty of time for your questions, so I hope you’ll join me at the event.

You can register for the regular monthly webinar here:

June Webinar Registrations

The details are:

CIAOPS Need to Know Webinar – June 2021
Friday 25th of June 2021
11.00am – 12.00am Sydney Time

All sessions are recorded and posted to the CIAOPS Academy.

The CIAOPS Need to Know Webinars are free to attend but if you want to receive the recording of the session you need to sign up as a CIAOPS patron which you can do here:

http://www.ciaopspatron.com

or purchase them individually at:

http://www.ciaopsacademy.com/

Also feel free at any stage to email me directly via director@ciaops.com with your webinar topic suggestions.

I’d also appreciate you sharing information about this webinar with anyone you feel may benefit from the session and I look forward to seeing you there.

IAMCP Video Presentation

I recently did a presentation for the International Association of Microsoft Channel Partners Quarterly Briefing and you can find the slides here:

https://www.slideshare.net/directorcia/microsoft-365-security-overview

The videos is also available now at:

https://www.youtube.com/watch?v=bGEfjgIfhdE

if you want to take a look.

Thanks again to the IAMCP for the opportunity to present on Microsoft cloud security.

CIAOPS Secwerks 1 registrations now open

pexels-pixabay-60504

With the venue now secured I am please to announce that registrations for CIAOPS Secwerks 1 in Melbourne CBD on Thursday August 5th and Friday August the 6th are now open. If you are not a CIAOPS Patron there is an early bird offer of $440 inc GST if you use the coupon code SWEB at check out. After that date, the price will be $798 inc GST. Note, costs exclude food which is not available in the venue. You can register now at:

https://www.ciaopsacademy.com/p/secwerks

The event is a 2 day hands on Level 400+ deep dive into security for Microsoft 365. It will cover topics such as:

– Exchange Online Security

– Windows 10 device hardening

– Incident monitoring and handling

– Effective identity security

– Data protection and more

If you have the responsibility for the management of Microsoft and Office 365 environments, then this session is for you.

I’ll be posting more information about the event in the coming weeks but if you do have questions please feel free to contact me via director@ciaops.com.

I look forward to seeing you at the event.

I need help with Windows Defender System Guard

I need some help in my question to enable Windows System Guard in my environment. If you want to know what it is see:

Hardening the system and maintaining integrity with Windows Defender System Guard

and the Microsoft article is here:

Windows Defender System Guard: How a hardware-based root of trust helps protect Windows 10

and in summary Windows System Guard is:

Windows Defender System Guard reorganizes the existing Windows 10 system integrity features under one roof and sets up the next set of investments in Windows security. It’s designed to make these security guarantees:
– Protect and maintain the integrity of the system as it starts up
– Validate that system integrity has truly been maintained through local and remote attestation

I enabled it using the techniques in this article:

System Guard Secure Launch and SMM protection

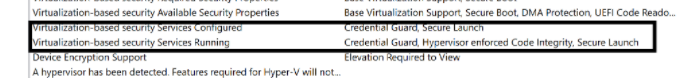
To verify it is enabled 9according to the article) you check MSInfor32 and you should see:

image

i.e. Secure Launch appear in both:

1. Virtualization based Security Configured

and

2. Virtualization based security Services Running

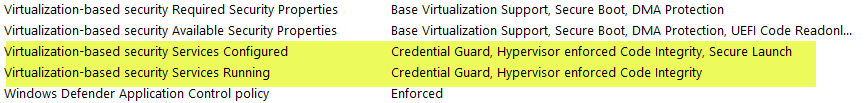
image

However, in my case I don’t see it appear under Virtualization based security Services Running as you see above?

Now, the Microsoft article does say:

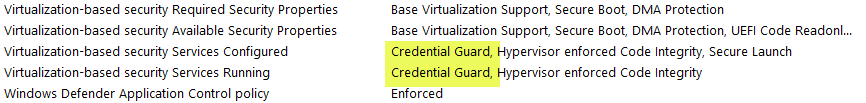
image

Credential Guard is definitely running per my MSInfo32

image

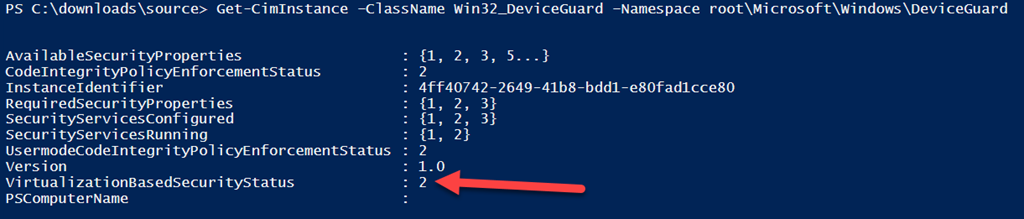
To check Virtualization Based Security I can run the command:

Get-CimInstance –ClassName Win32_DeviceGuard –Namespace root\Microsoft\Windows\DeviceGuard


and I see the following:

image

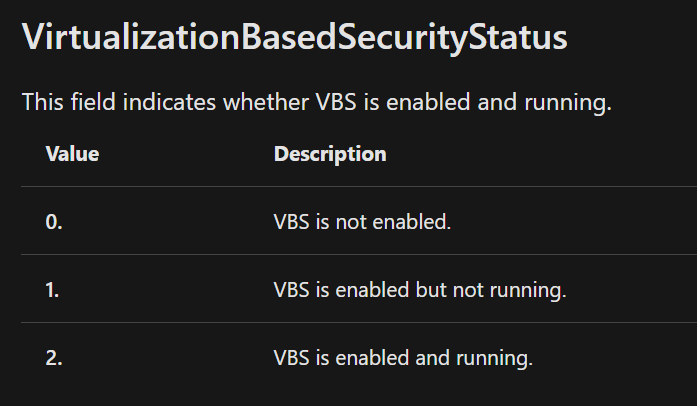
According to the documentation,

image

if VirtualizationBasedSecurityStatus = 2 then:

VBS is enabled and running

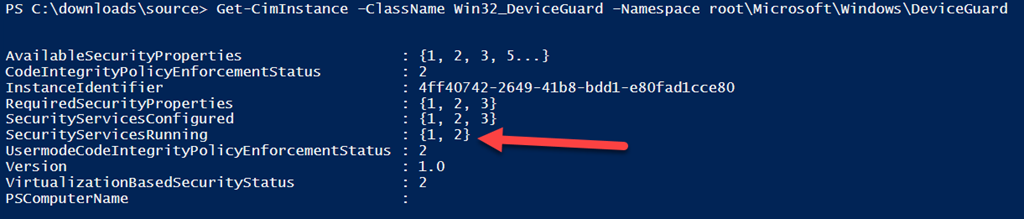
Now, if I look at the SecurityServicesRunning field I see:

image

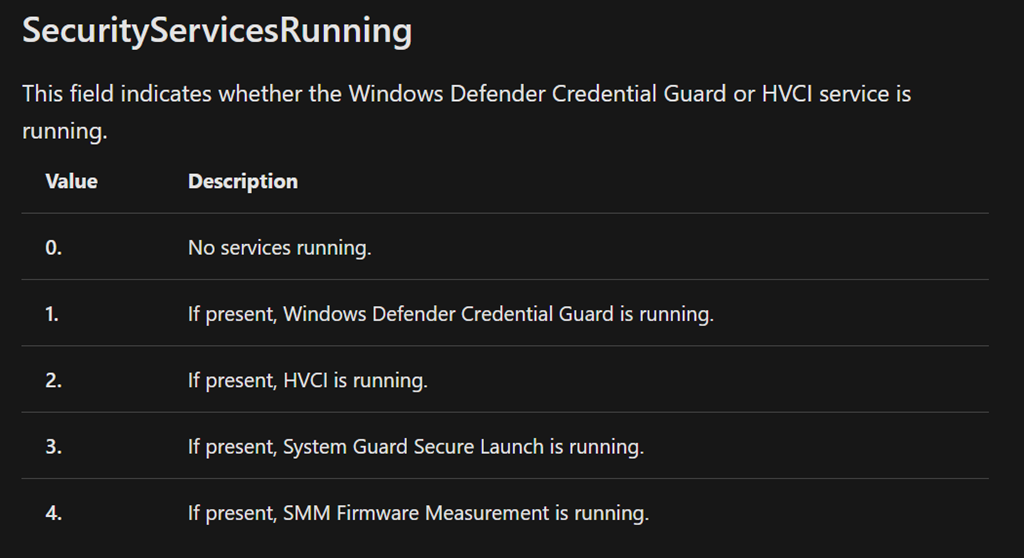
only Credential Guard and HVCI running per:

image

i.e no System Guard Secure launch. This confirms what I see in MSInfo32.

Verifying Device Guard is where things get challenging, because this:

Why we no longer use the Device Guard brand

seems to indicated the device Guard is now Windows Defender Application Control (WDAC)??

However, there is this article:

Windows 10 Device Guard and Credential Guard Demystified

from early 2021 talking about Device Guard?? Here, Device Guard is:

Now that we have an understanding of Virtual Secure Mode, we can begin to discuss Device Guard. The most important thing to realize is that Device Guard is not a feature; rather it is a set of features designed to work together to prevent and eliminate untrusted code from running on a Windows 10 system

Device Guard consists of three primary components:

  • Configurable Code Integrity (CCI) – Ensures that only trusted code runs from the boot loader onwards.

  • VSM Protected Code Integrity – Moves Kernel Mode Code Integrity (KMCI) and Hypervisor Code Integrity (HVCI) components into VSM, hardening them from attack.

  • Platform and UEFI Secure Boot – Ensuring the boot binaries and UEFI firmware are signed and have not been tampered with.

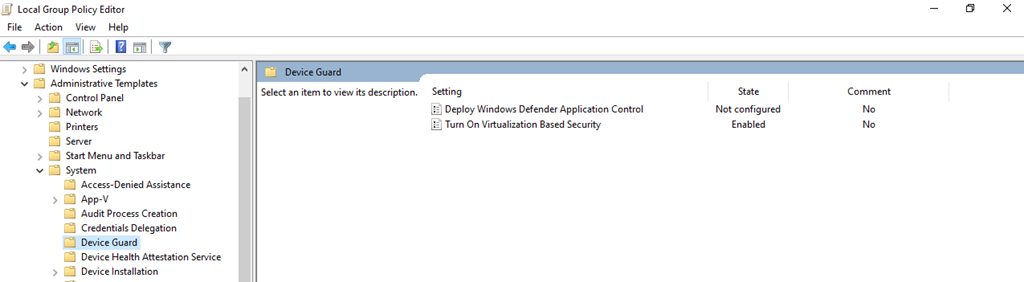
According to that article the CCI is located at:

Computer Configuration \ Administrative Templates \ System \ Device Guard \ Deploy Code Integrity Policy

image

But I can’t see that on my machine as shown above??

I can’t see how to specifically enabled VSM Protected Code Integrity, I can only find:

Code Integrity

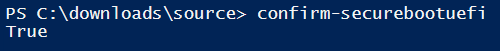
Finally, my machine does have UEFI and secure boot enabled:

image

The last piece of the puzzle is a service called Secure Launch:

image

which I have running and seems to be linked to System Guard but I can find no confirmation of what this service actually does??

In summary, I am at a loss to understand why my machine seems to not have System Guard enabled even though it is capable it seems. I feel confident that I do have all the requirements in place but the Configurable Code Integrity (CCI) may be the issue but I can’t find anything on how to configure that.

My ask then, is if you have any information on helping me get System Guard working on my machine or help me understand why it isn’t working I’d appreciate it as I have drawn a blank with all my other sources.